Three Lines Enforcement
Strict segregation between first-line business units, second-line risk/compliance oversight, and third-line internal audit.
Purpose-built for banks managing complex central bank circulars, prudential requirements, and operational risk. Designed around Basel Committee PSMOR, COSO, UAE NCAP, and SBP regulatory expectations.
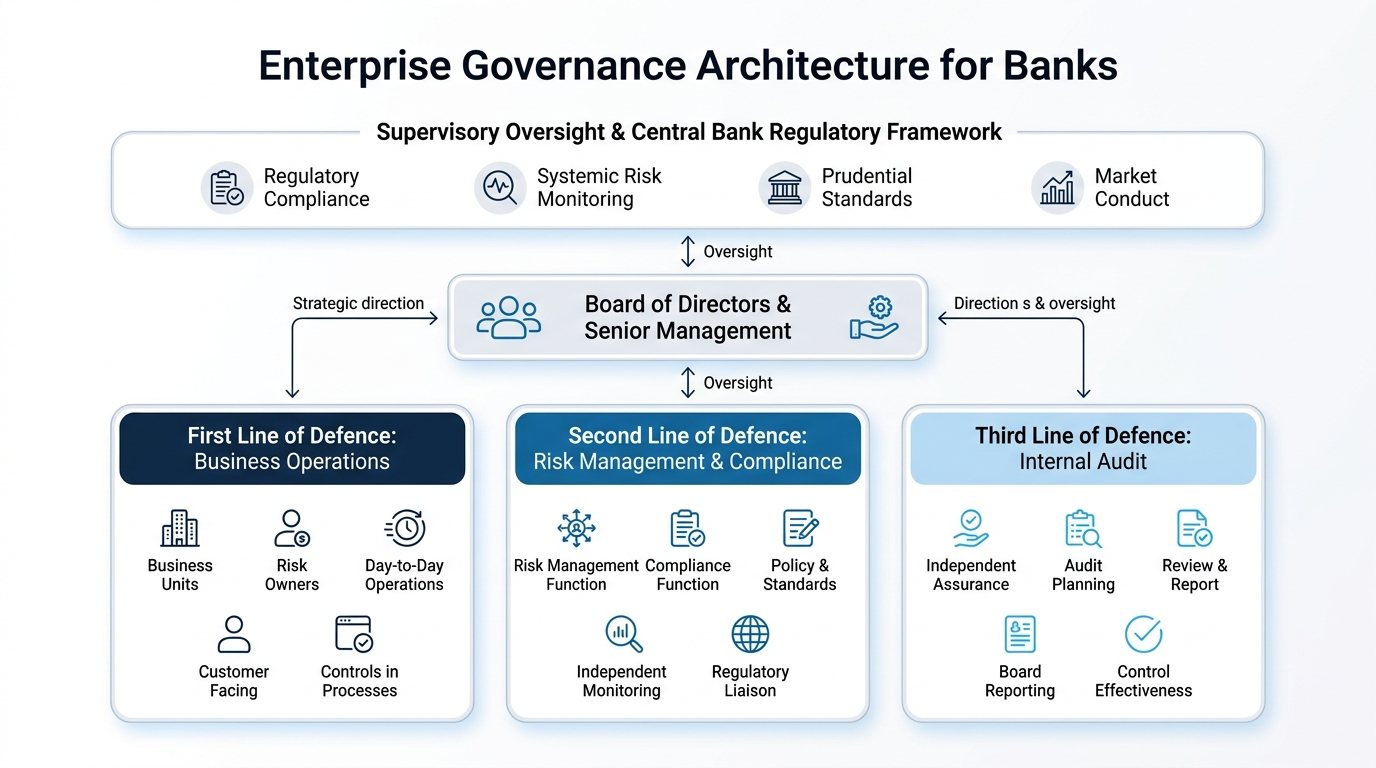
Enterprise banking governance: Supervisory oversight integrated with 1LOD, 2LOD, and 3LOD roles.
Financial institutions face intense scrutiny from central banks and regulatory authorities requiring continuous, evidenced control effectiveness.
Strict segregation between first-line business units, second-line risk/compliance oversight, and third-line internal audit.
Deployment architecture, data-residency and private-infrastructure requirements can be assessed as part of enterprise solution design.
Maintain pre-built examination workspaces to respond quickly to regulator requests with timestamped submission bundles.
Schedule an executive briefing with our banking GRC specialists.