Broken Traceability
Obligations, controls, risks, and findings live in siloes, making it impossible to trace a supervisory finding back to the control that failed.
OrviQ connects regulatory obligations directly to controls, verified evidence, and independent challenge, ensuring control assurance is continuously documented rather than reconstructed during examinations.
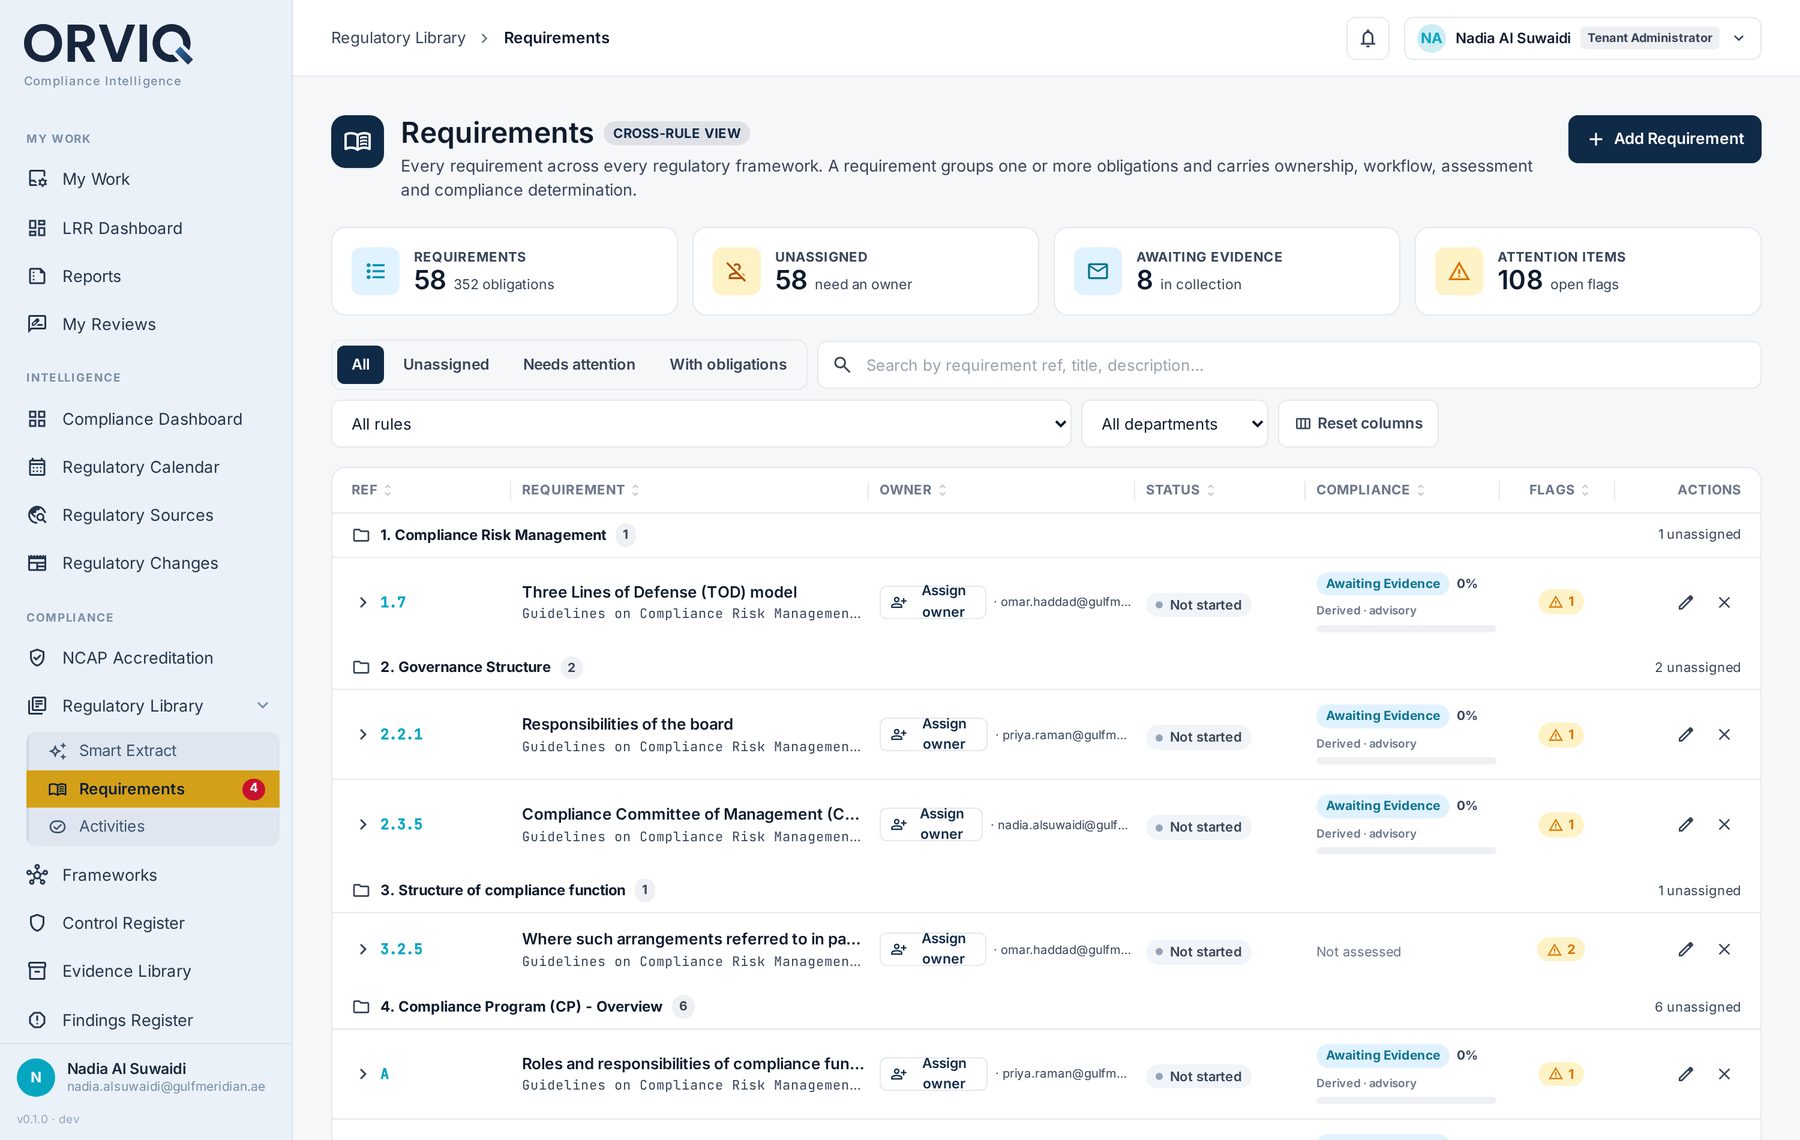
Every requirement, one register, named ownership, and verified audit trail.
Spreadsheets for circulars, disconnected portals for policies, and manual trackers for audit findings leave institutions unable to demonstrate control effectiveness.
Obligations, controls, risks, and findings live in siloes, making it impossible to trace a supervisory finding back to the control that failed.
Spreadsheets cannot enforce segregation of duties or independent challenge, allowing self-assessments to pass without validation.
Board packs and regulator submissions are assembled manually from point-in-time files rather than derived from a live system of record.
Each module is licensed per tenant, sharing a unified data model that connects regulations, controls, evidence, and risk.
Decompose circulars into discrete obligations and track regulatory changes in real time.
Dual-axis design and operating effectiveness assessments with RCSA campaign waves.
A centralized control repository with deterministic evidence freshness lifecycles.
Risk and KRI registers with explicit appetite monitoring and residual risk tracking.
Deficiency management with configurable governed approval workflows and SLA tracking.
Versioned policy library with gap analysis against regulatory obligations.
Audit workpapers, independent 3LOD findings, and evidenced corrective action plans.
Examination workspaces from supervisory notice to closure with observation tracking.
Critical business services, dependency mapping, BIA, and recovery scenario testing.
Schedule an architecture walkthrough with our product team.